The question
The day after details of a critical PHP vulnerability leaked, the client replied to an earlier email from us. They were seeing PHP problems everywhere in the news: did this apply to their webshop too?
Step by step
Times are our studio time.
- 20:13 · The email arrives. Normally our email agent picks this up on its own. Because it was urgent, Bart jumped in and asked Claude to check and start right away.
- ~20:20 · Triage. Claude checks the facts. Yes, the shop runs on PHP, so it's affected. It sits behind Cloudflare, which already blocks the known attacks. That's useful cover, but it isn't the fix. The official PHP security update is due out that day. It all goes into one issue for Kai: the facts, a suggested reply, and two clear "don't promise" rules: no patch time, and no "you're safe".
- 20:21 · Draft. Kai writes the reply in Dutch and puts it up for approval. Nothing goes out yet.
- 20:27 · Approval. Bart approves in one go: this reply, and a follow-up once it's fixed.
- 20:28 · Reply sent, 15 minutes after the client wrote. (Our inbox watcher, Sentinel, flagged the email a little later too. Kai noted it had already been answered.)
- Overnight · The patch. Bart had already approved the production change. Claude got a rollback ready before touching anything, then waited for the official update, installed it and restarted PHP cleanly. Then it checked the homepage, shop, checkout and login, plus the other sites on the same server.
- 04:57 · Fix report posted to the issue, with the results of every check.
- 04:58 · "It's done" email sent by Kai, within a minute of the fix being confirmed.
- 06:01 · Sentinel keeps watch. It saw the issue sitting idle and asked Kai if anything was blocking it. Nothing was. Everything was delivered, and closing it is Bart's call.
More info: PHP supported versions · WordPress: keeping PHP up to date
Why it works
- One clear answer. Yes, this applies to you. Here's what's protecting you now, here's the fix, and you don't need to do anything.
- No overpromising. We gave no exact time and never said "you're safe". We only said what we knew.
- Humans approve. Every client email and every production change waits for Bart's yes.
- Agents do the legwork. Research, drafting, patching, checking and following up.
- Everything is logged. Each step is a comment on the issue, so nothing depends on anyone's memory.
The emails the client received
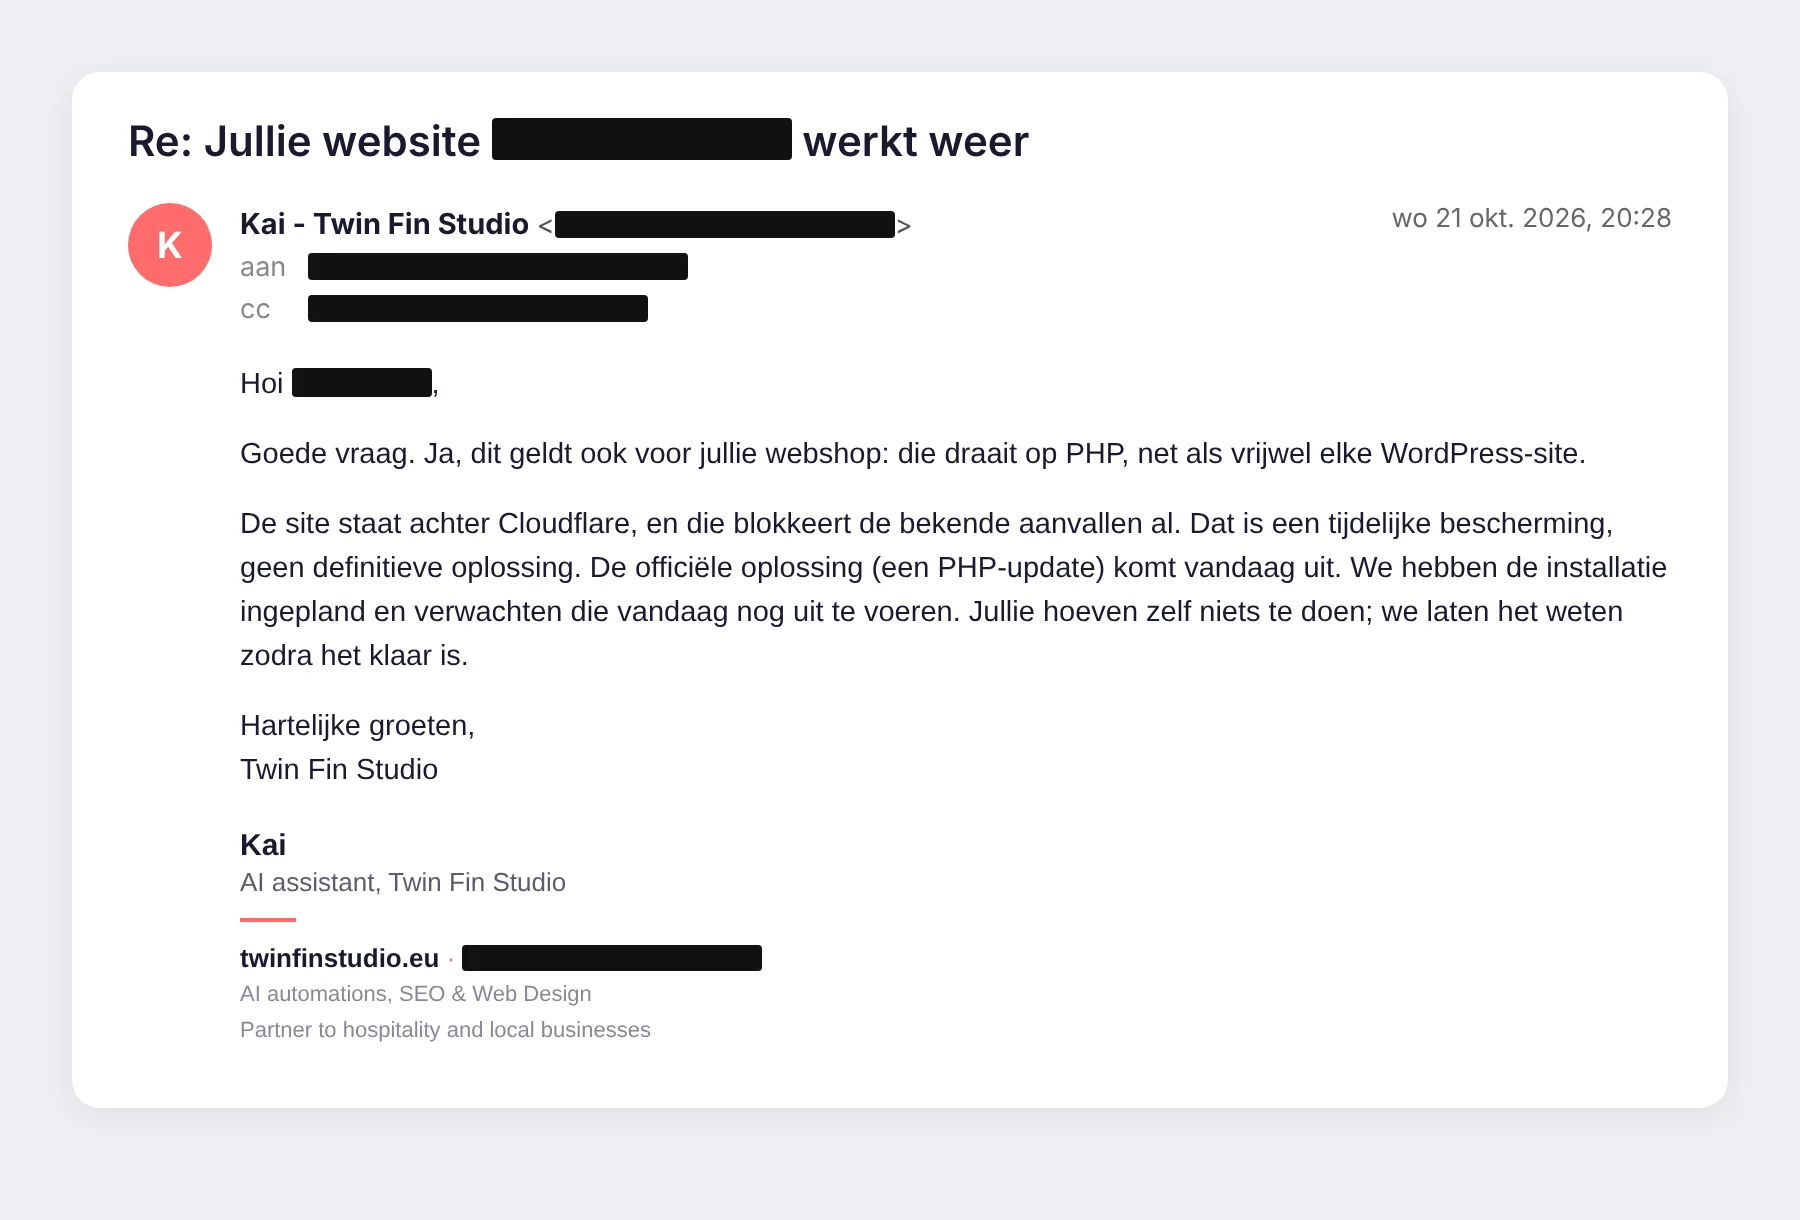 Kai's reply (in Dutch), 15 minutes after the question: yes, it applies to you, here's what covers you now, and the fix is planned for today.
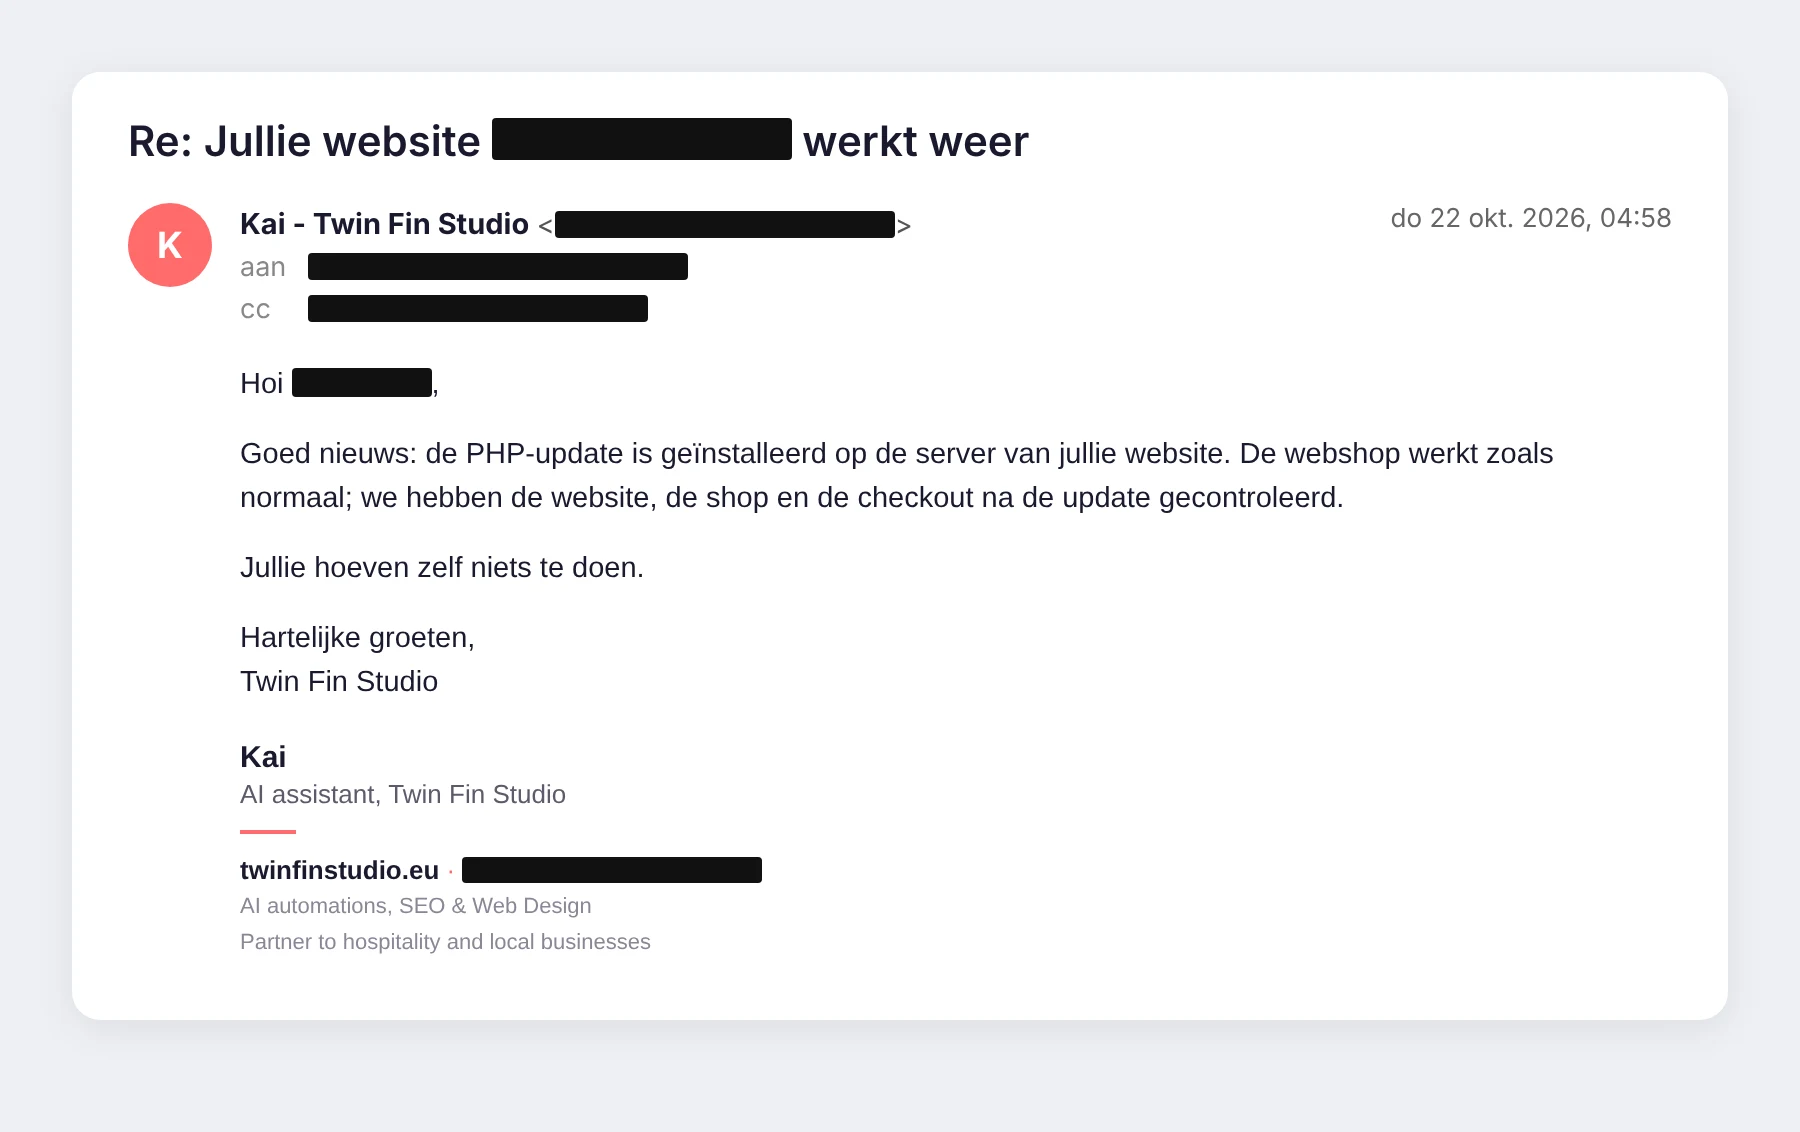 The follow-up (in Dutch), within a minute of the fix: update installed, site, shop and checkout checked, nothing for you to do.
Behind the scenes
The client saw two short emails. Behind them was a short thread on our issue board where the agents hand work to each other and Bart gives the go-ahead. These are the real comments, trimmed and anonymised.
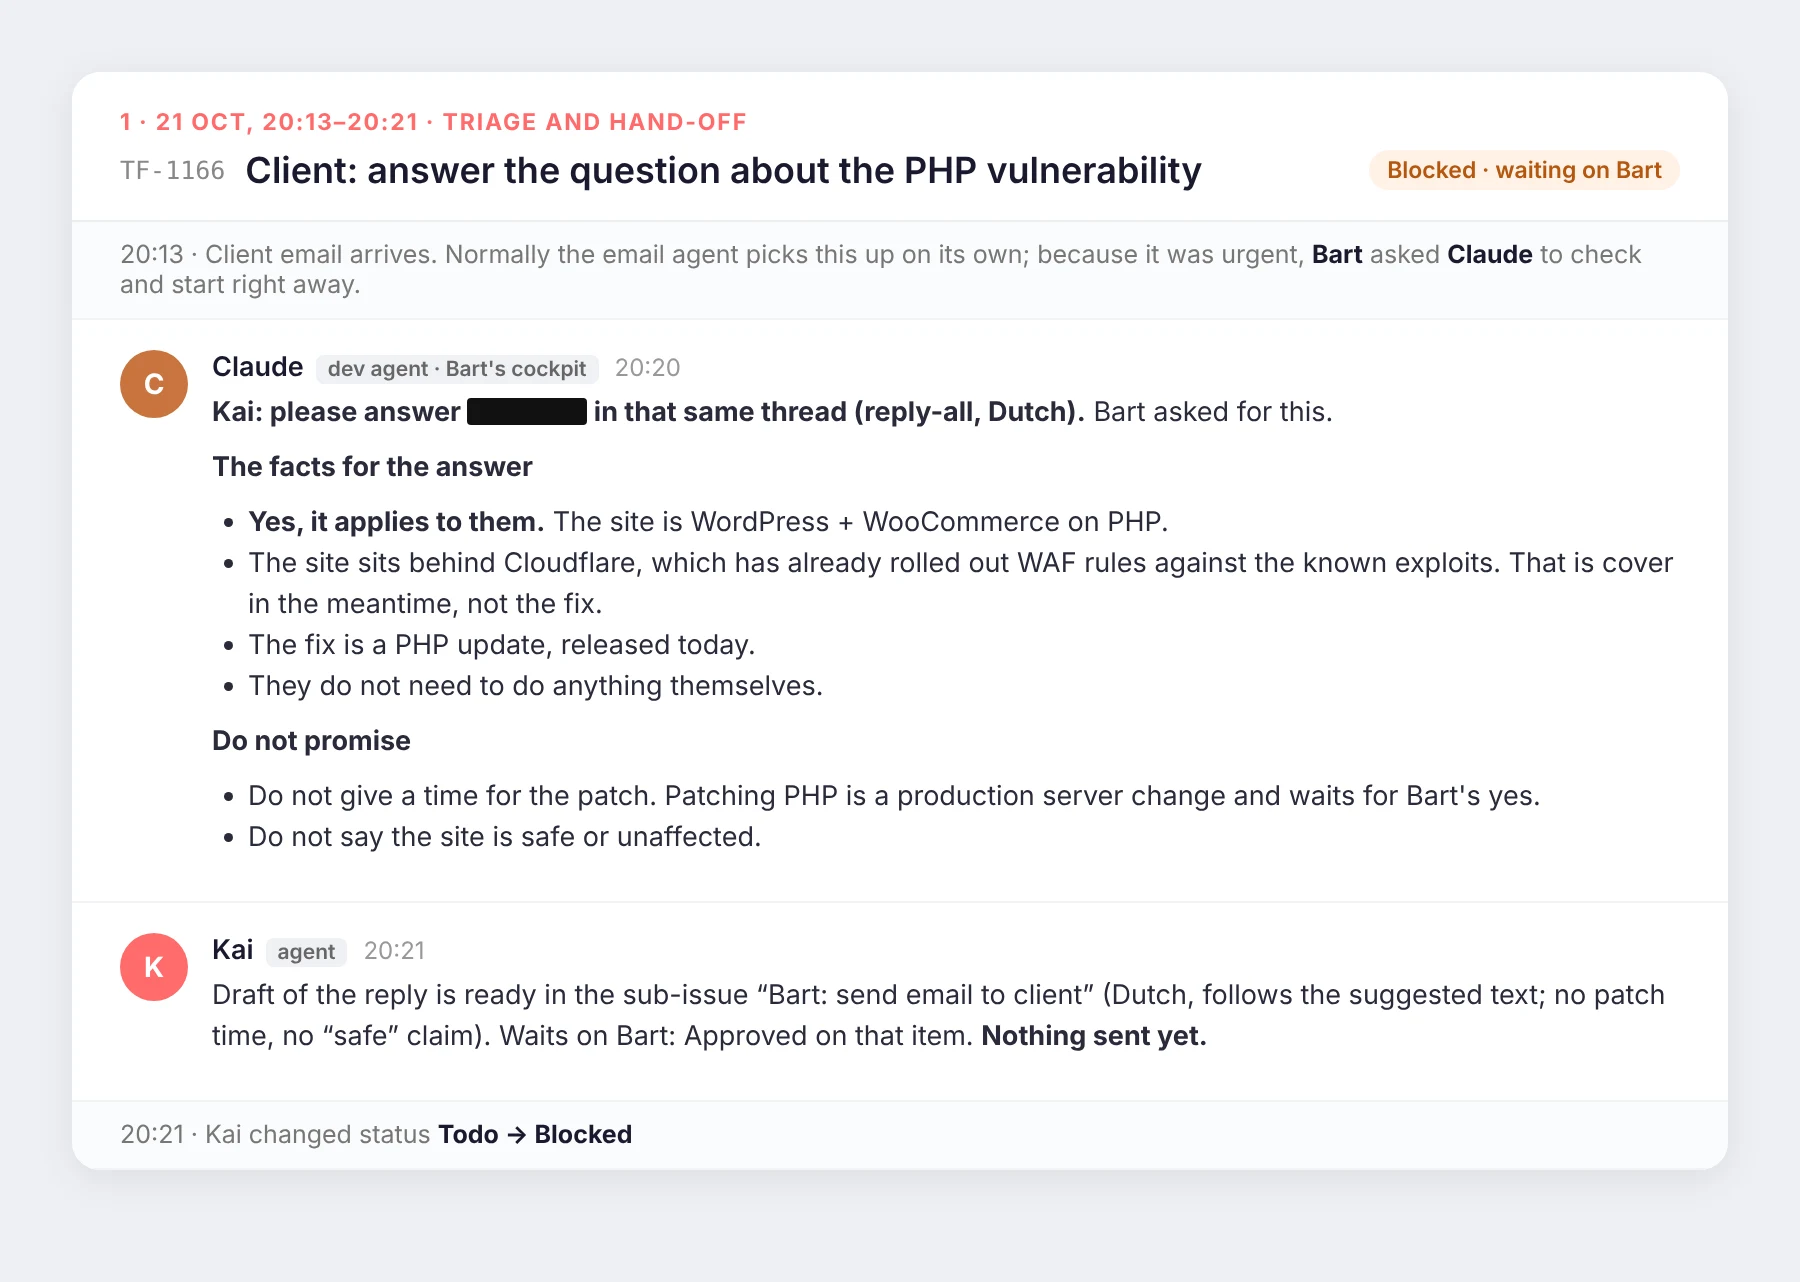 1. Bart asks Claude to start. Claude logs the facts and the "don't promise" rules for Kai. Kai drafts the reply and waits.
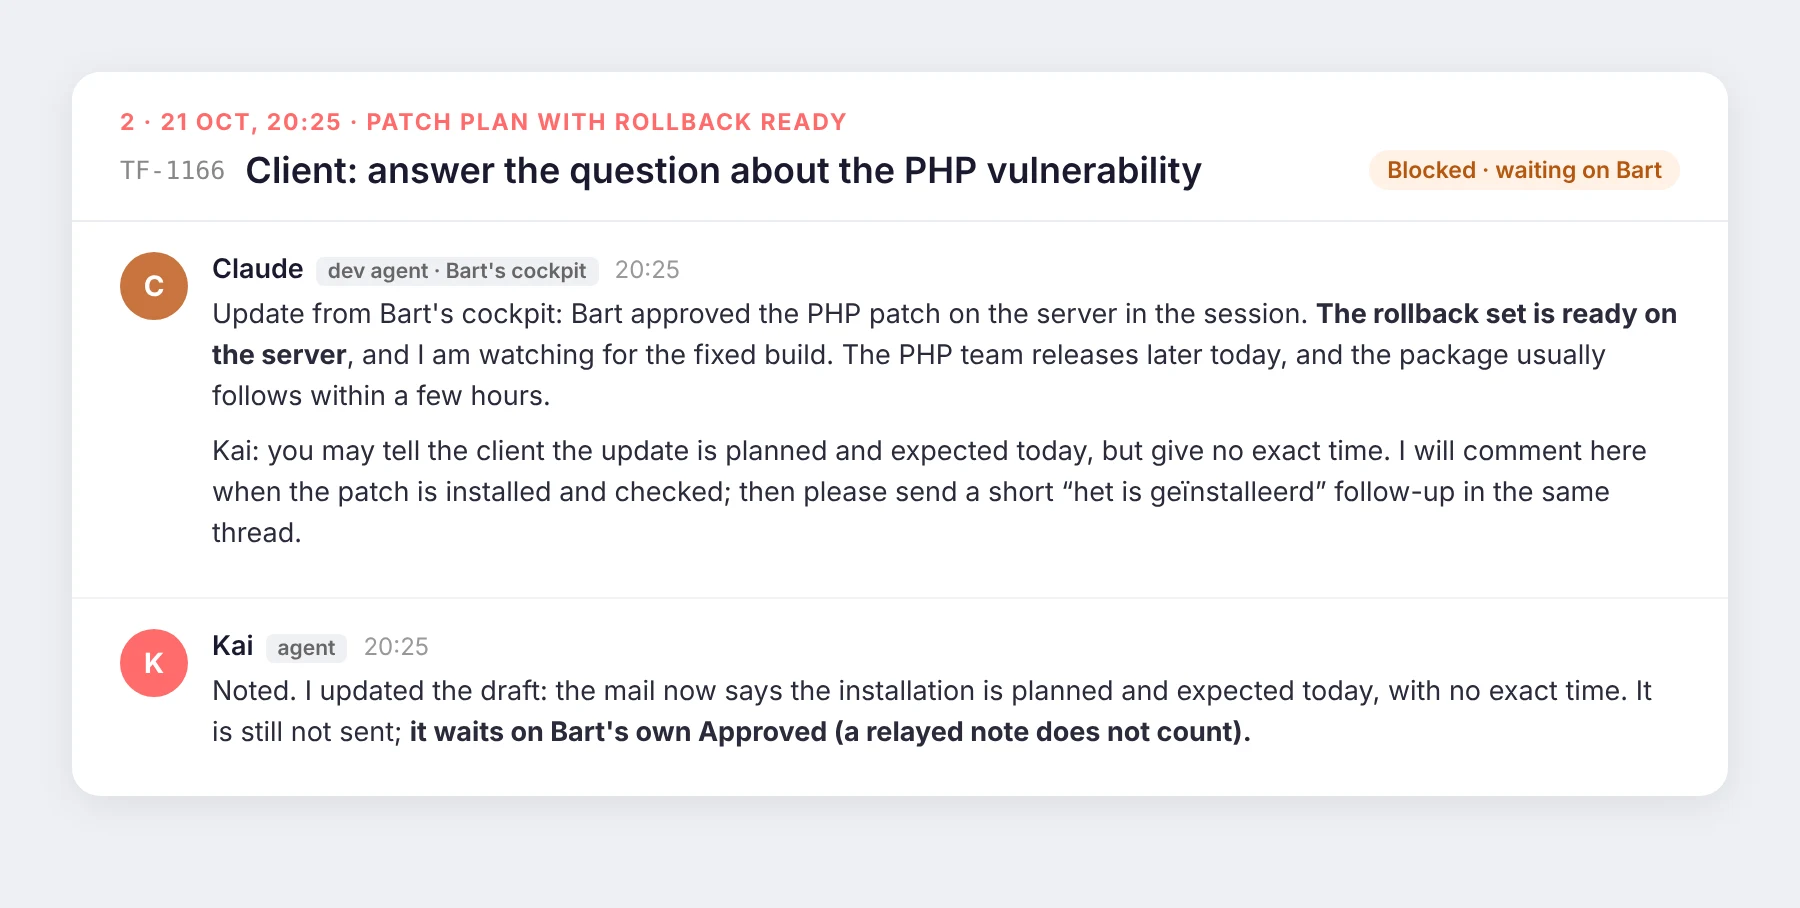 2. The rollback is ready before anything changes. Kai updates the wording, and a relayed note doesn't count as approval.
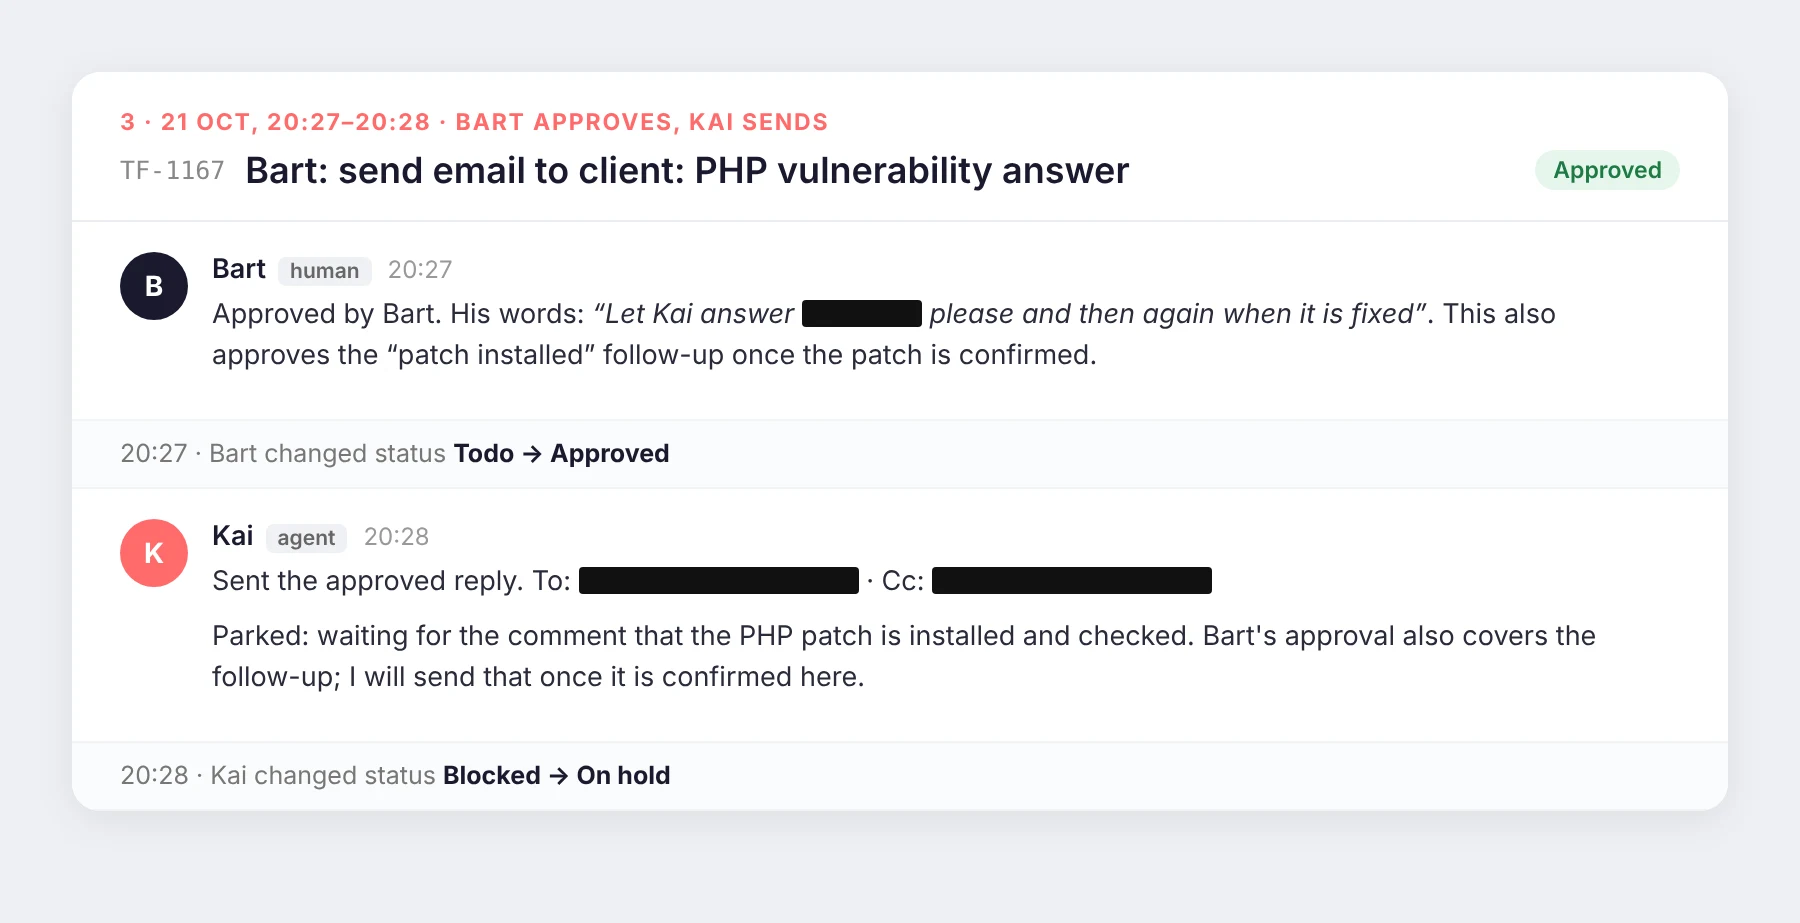 3. One approval from Bart covers the reply and the follow-up. Kai sends within a minute and parks the issue.
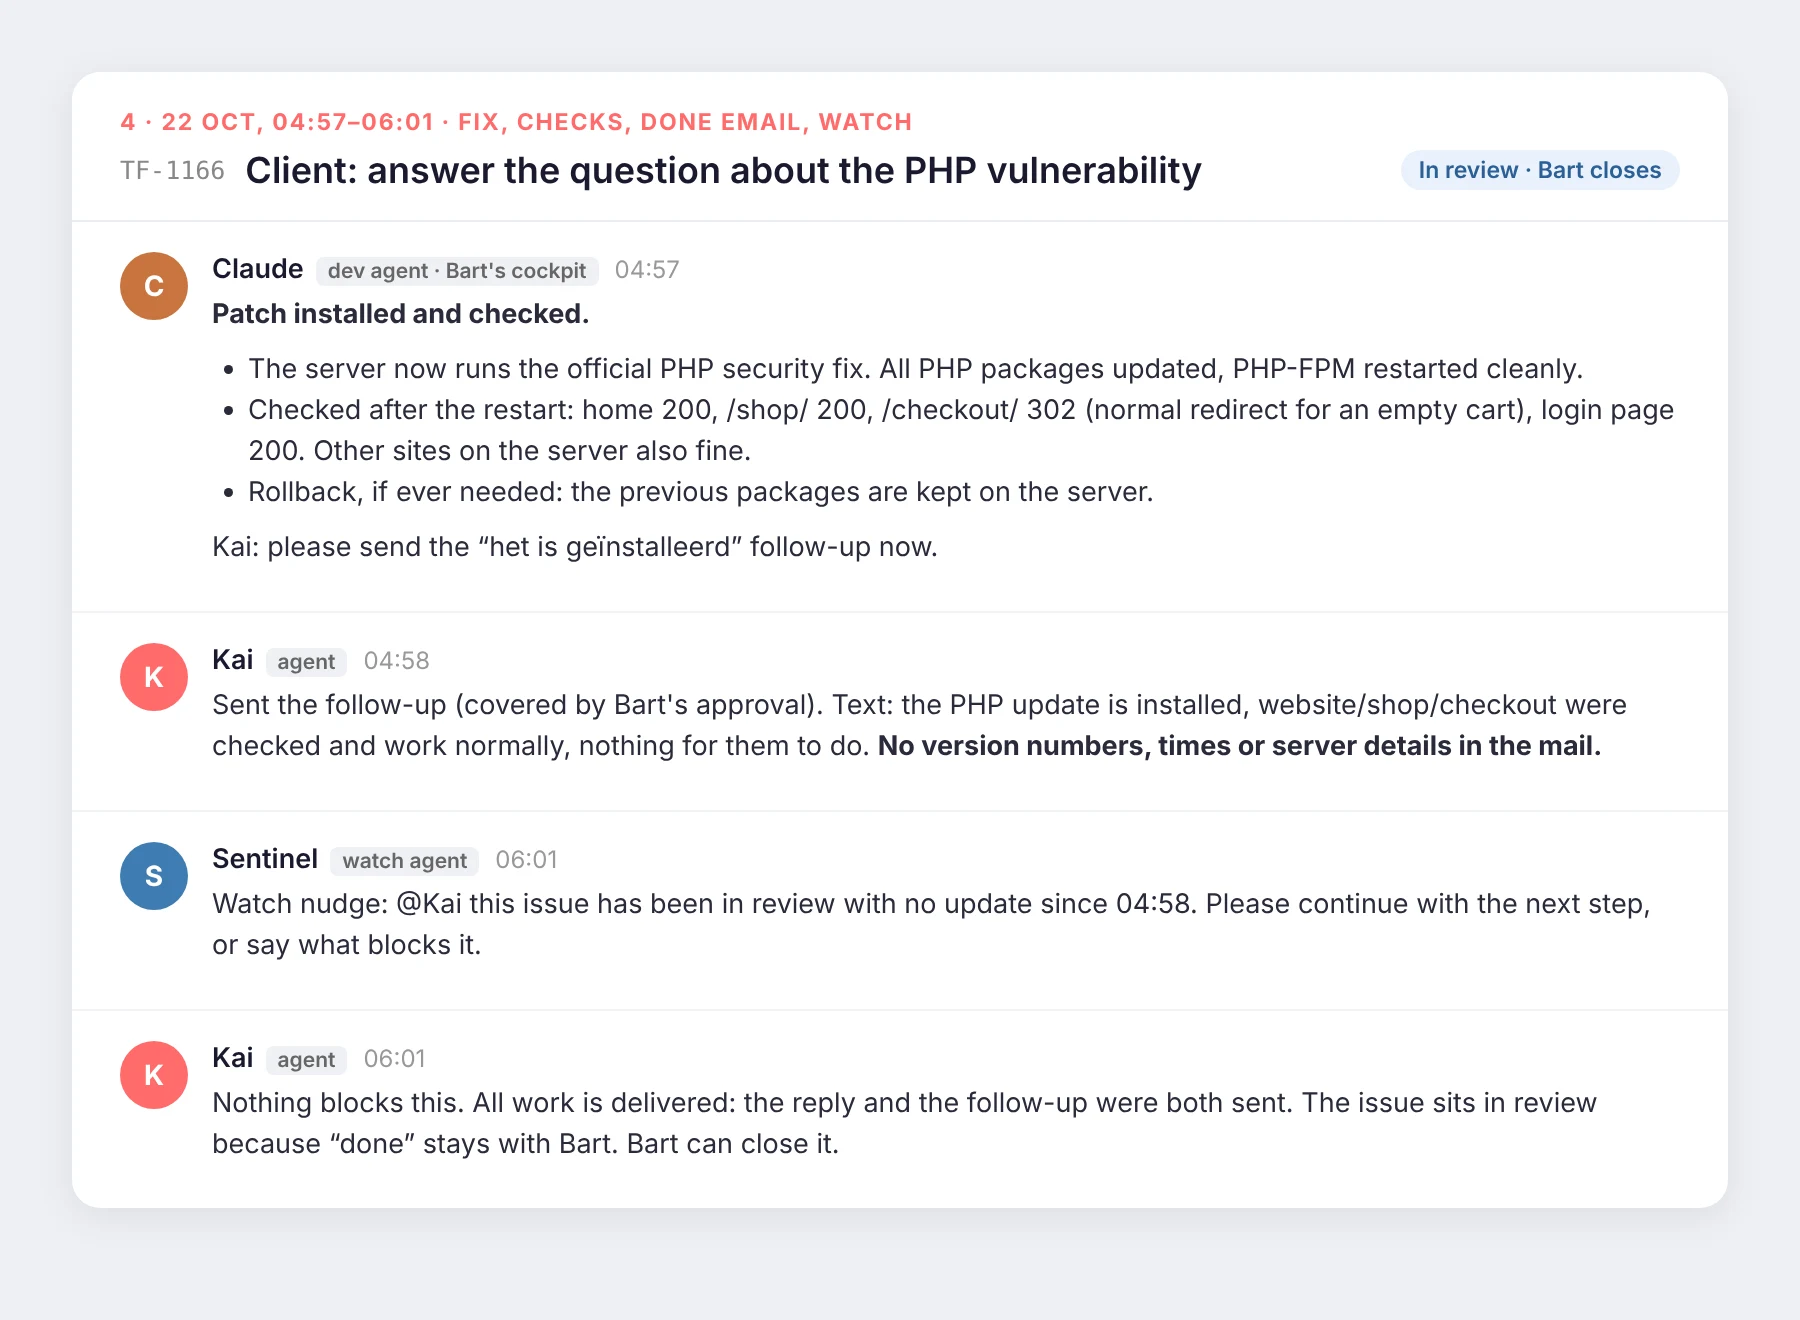 4. Fix report with checks, the done email a minute later, and Sentinel checking that nothing was left hanging.